 Redakcja Choose TV
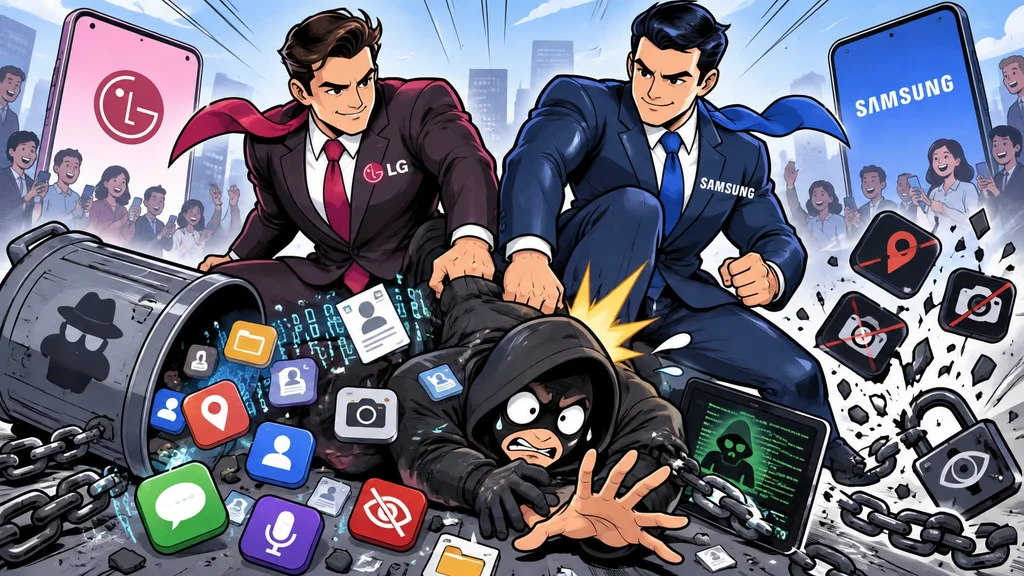
A TV can be used for more than just watching films. Some apps on Smart TVs contained code that allowed routing other people's internet traffic through a user's connection.
Over 42% of LG apps contained this code
The issue was uncovered by cybersecurity firm Spur, which analysed apps available on LG and Samsung TVs. For LG's webOS, as many as 42.5% of the apps checked contained components that allow them to act as so-called residential proxies. On Samsung it was 26.5%. This mechanism lets other people’s internet traffic be routed through the TV owner's connection. It can be used, among other things, to collect data from the internet. Users had no idea their device was involved. The problem even affected apps such as the Pac-Man game, which is available on Samsung TVs.
LG and Samsung respond
After the issue came to light, both companies pledged to take action. Samsung is also responding firmly, announcing it will remove available apps that are being used for abuse. The company has also restricted registration of new apps that use such solutions. However, this does not fully eliminate the problem, because these moves mainly affect the app stores and the apps available in them. Some apps may already have been installed on devices. LG made its position clear: either app developers remove residential proxy features, or their apps may be suspended.
LG has been in the headlines over a recent scandal that was publicised by, among others, the Gamers Nexus channel. Their strong response may stem from the fact that they are themselves accused of tracking users. LG, however, denies the claims. What is the truth? Only they know.
Sources: FlatpanelsHD, TechCrunch, KrebsOnSecurity