 Redakcja Choose TV
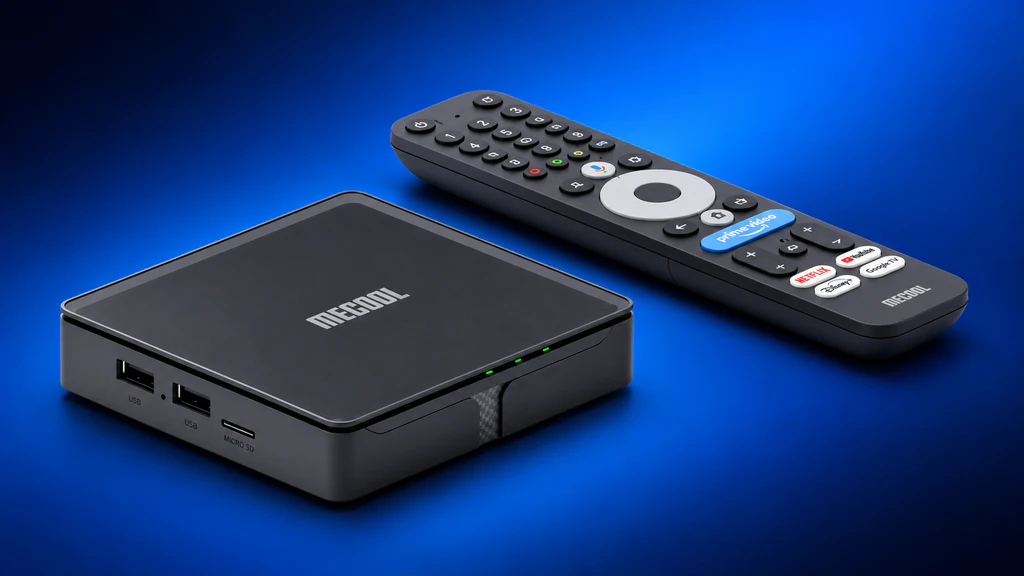
Google revealed a serious security problem with Android TV set-top boxes. More than 1.3 million devices were enrolled in a botnet that allowed cybercriminals to use them without their owners' knowledge. Most surprisingly, the malware was reportedly deliberately installed by the manufacturer itself, and some devices even carried an official Google certificate.
Manufacturer intentionally installed malware
According to Google Threat Intelligence Group, the scheme was carried out by Chinese company Videostrong Technology, which manufactures TV set-top boxes under brands including Mecool.
The devices' software contained a backdoor called XCPE, which allowed remote installation of apps, data interception, and the use of a home internet connection for illegal activities. Infected boxes were used for ad fraud and redirecting internet traffic.
Interestingly, some devices had Google Play Protect certification. The malware bypassed security checks because its additional components were downloaded only after the device's first boot.
Google responds. What about users?
Google, together with partners, has shut down the infrastructure used to manage the botnet. The company also cut ties with Videostrong, barring the manufacturer from producing certified devices with Google services.
That does not mean the problem has completely gone away. Malware can still reside in the memory of infected devices, and simply removing it is not always possible.
People using Mecool set-top boxes or other devices from Videostrong should check their model and the availability of secure firmware. If an infection is suspected, it’s best to disconnect the device from the internet and contact the manufacturer.
It’s worth stressing that the issue concerns specific devices and their firmware, not all televisions running Android TV or Google TV.
Sources: FlatpanelsHD, Google, Malwarebytes